Julia Chirkova
The Treasury Inspector General for Tax Administration (TIGTA) has issued a stark assessment of the Internal Revenue Service’s (IRS) cybersecurity program, declaring it "not effective" for Fiscal Year 2026. This determination stems from significant shortcomings in three critical functional areas: IDENTIFY, PROTECT, and DETECT, which failed to achieve an acceptable overall maturity level. The findings, mandated by the Federal Information Security Modernization Act of 2014 (FISMA), highlight persistent vulnerabilities that could jeopardize taxpayer data.
TIGTA’s Annual Mandate and the IRS’s Performance
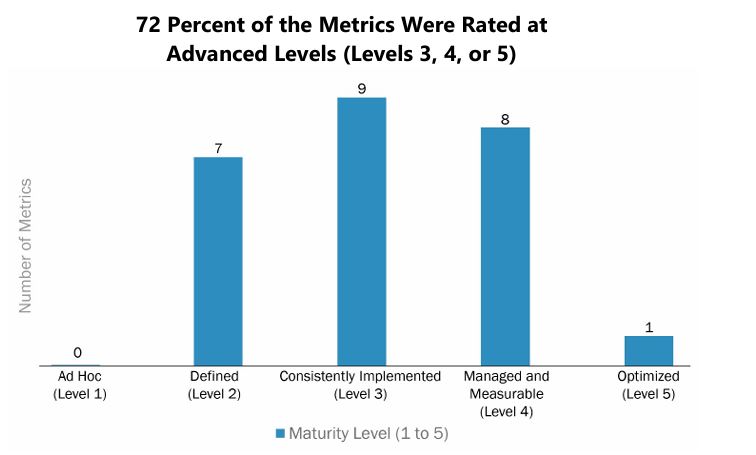
FISMA requires federal agencies to undergo annual assessments of their information security programs and practices. TIGTA, in its role as an oversight body for the Department of the Treasury, conducts these evaluations to ensure compliance and identify areas for improvement. For Fiscal Year 2026, TIGTA employed a rigorous methodology, testing 20 core reporting metrics, 5 supplemental metrics, and 10 editorial metrics. These metrics are designed to gauge the effectiveness of an agency’s cybersecurity posture, with "effective" defined as achieving a maturity Level 4 (Managed and Measurable) or higher.
While the IRS has demonstrated some progress compared to previous fiscal years, the TIGTA report underscores that these improvements are insufficient to meet FISMA’s stringent requirements. The report explicitly states that "IRS Cybersecurity management needs to fully implement all security program components in compliance with FISMA requirements." This directive points to a systemic need for more robust and comprehensive application of security protocols across the agency.
Key Areas of Concern: IDENTIFY, PROTECT, and DETECT
The core of TIGTA’s finding of ineffectiveness lies in the underperformance of three fundamental cybersecurity functions:
- IDENTIFY: This function encompasses the processes and activities to manage cybersecurity risk to organizational operations, organizational assets, individuals, other organizations, and the Nation. It involves understanding an organization’s assets, risks, and vulnerabilities. The IRS’s deficiency in this area suggests a potential lack of comprehensive asset inventory, risk assessment, or a failure to fully understand the threat landscape it faces.
- PROTECT: This function focuses on implementing appropriate safeguards to ensure the delivery of critical services. It includes access control, data security, and maintenance, among other measures. Shortfalls here indicate that the IRS may not be adequately protecting its systems and data from unauthorized access or modification.
- DETECT: This function involves implementing activities to identify the occurrence of a cybersecurity event. This includes continuous monitoring, intrusion detection, and anomaly detection. A lack of effectiveness in this area means the IRS may be slow to identify and respond to security breaches, increasing the potential for damage and data exfiltration.
In contrast, the IRS’s performance in the GOVERN, RESPOND, and RECOVER functions was deemed effective. The "GOVERN" function relates to the management of cybersecurity risk and the establishment of policies and procedures. "RESPOND" deals with the actions taken when a cybersecurity incident is detected, and "RECOVER" focuses on maintaining resilience and restoring capabilities or services that were impaired due to a cybersecurity incident. The effectiveness in these areas suggests that the IRS has established frameworks for managing incidents and recovering from them, but the foundational elements of identifying and protecting assets, and detecting threats, remain weak.
The Gravity of Unresolved Vulnerabilities: A Threat to Taxpayer Data
The TIGTA report provides a concrete example of the severity of the IRS’s security lapses: "86 percent (6 out of 7) of the sampled information systems had critical vulnerabilities not remediated within 30 days, as required." This statistic is particularly alarming, as it indicates a widespread failure to address known security flaws in a timely manner. Critical vulnerabilities, if left unaddressed, can serve as entry points for malicious actors seeking to compromise systems and access sensitive information.
The direct implication of these ongoing deficiencies is the heightened risk to taxpayer data. The report warns that "If the IRS does not take steps to mitigate these deficiencies, taxpayer data could be vulnerable to inappropriate and undetected use, modification, or disclosure." This scenario represents a profound breach of public trust and could have severe consequences for millions of individuals and businesses whose financial information is handled by the IRS. The potential for identity theft, financial fraud, and the exposure of sensitive personal and financial details is a significant concern for both taxpayers and national security.
Background: The Evolving Threat Landscape and FISMA’s Role
The Federal Information Security Modernization Act of 2014 was enacted to strengthen the federal government’s cybersecurity posture in response to an increasingly sophisticated threat landscape. Prior to FISMA, cybersecurity oversight was often fragmented, leading to inconsistencies in agency security practices. FISMA aimed to centralize and enhance these efforts by requiring agencies to develop and implement comprehensive information security programs, conduct regular risk assessments, and report on their security performance.
The IRS, as the primary tax collection agency of the United States, handles an immense volume of highly sensitive personal and financial data. This makes it a prime target for cybercriminals and state-sponsored actors. The agency has faced scrutiny over its cybersecurity practices for years, with previous reports from TIGTA and the Government Accountability Office (GAO) highlighting areas for improvement. The recurring nature of these findings suggests that the IRS faces ongoing challenges in adapting its security infrastructure and practices to keep pace with evolving cyber threats.
The IRS’s Responsibility and the Path Forward
While TIGTA’s role is to report on performance metrics and not to make specific recommendations, the implications of its findings are clear. The IRS leadership must prioritize the full implementation of all security program components mandated by FISMA. This will likely involve a multi-faceted approach:
- Enhanced Investment: A significant increase in investment in cybersecurity infrastructure, technology, and personnel may be necessary. This could include upgrading legacy systems, adopting advanced threat detection and response capabilities, and bolstering the agency’s cybersecurity workforce with skilled professionals.
- Strengthened Policies and Procedures: A thorough review and update of existing cybersecurity policies and procedures will be crucial. This includes ensuring that policies are not only comprehensive but also effectively communicated and enforced across all levels of the organization.
- Improved Training and Awareness: Continuous training for all IRS employees on cybersecurity best practices, threat awareness, and data handling protocols is essential. Human error remains a significant factor in many security breaches, and a well-informed workforce can act as a critical line of defense.
- Proactive Vulnerability Management: The agency must develop and adhere to more stringent timelines for identifying and remediating vulnerabilities. This requires robust scanning and testing protocols, as well as a clear process for prioritizing and addressing critical security flaws.
- Continuous Monitoring and Evaluation: The IRS needs to implement comprehensive continuous monitoring programs to detect anomalous activity and potential breaches in real-time. Regular internal audits and independent assessments will be vital to ensure ongoing compliance and identify emerging risks.
Broader Implications and Public Trust
The cybersecurity posture of the IRS has far-reaching implications beyond just the agency itself. A compromised IRS could lead to widespread identity theft, economic disruption, and a significant erosion of public trust in government institutions. Taxpayers entrust the IRS with their most sensitive financial information, and any perceived inability to protect this data can have a chilling effect on voluntary tax compliance.
The effectiveness of the IRS’s cybersecurity program is not just a technical issue; it is a matter of national security and economic stability. The agency’s ability to fulfill its mission depends on its capacity to safeguard the data it collects and manages. The TIGTA’s report serves as a critical alert, underscoring the urgent need for the IRS to address these systemic weaknesses and ensure the integrity and confidentiality of taxpayer information.
The full report, titled "The IRS’s Cybersecurity Program Was Not Effective for Fiscal Year 2026," is publicly available on TIGTA’s website, offering a detailed account of the assessment and its findings. The document provides the basis for understanding the specific challenges the IRS faces and the imperative for decisive action.
The IRS has acknowledged the importance of cybersecurity and has stated its commitment to protecting taxpayer data. However, the findings of the TIGTA report indicate that substantial work remains to be done to achieve a truly effective cybersecurity program. The coming fiscal years will be crucial in demonstrating whether the agency can successfully implement the necessary improvements to fortify its defenses against the ever-evolving threats in the digital realm. The security of millions of American taxpayers’ data hinges on their success.